On this page
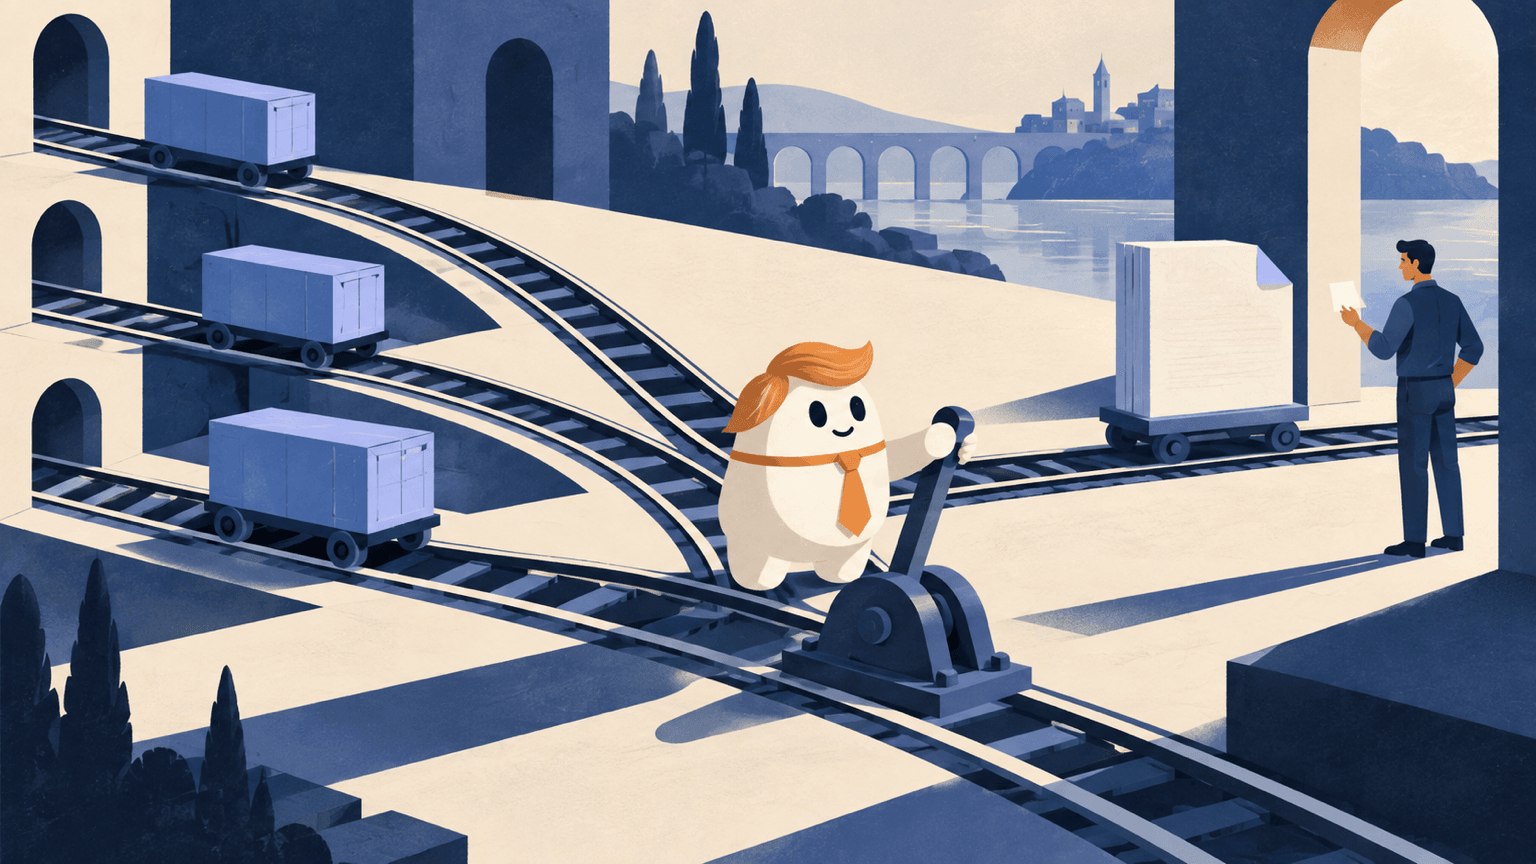
Agent orchestration can feel abstract until a workflow fails three steps in and nobody can say which agent was responsible. Most teams lose time wiring agents together before deciding who controls routing, state, and recovery. This guide covers what orchestration is, how the control loop runs, the main patterns worth choosing from, and the controls to add before scaling autonomy.
What agent orchestration is—and what it is not
Readers who search for "ai agent orchestration a complete guide" usually want two things at once: a definition they can repeat, and a way to make decisions. Here is the short version. AI agent orchestration is the control layer that turns a high-level objective into ordered, observable execution.
It decides when models and tools run, what context each step receives, how state changes, and when work retries, pauses, hands off, or stops.
The term sits near several others that are easy to confuse:
- An LLM generates text in response to a prompt. It does not decide workflow order, track state between steps, or know when to stop.
- An agent pairs a model with tools and instructions to pursue a task. It acts, but something else governs the conditions it acts under.
- The agent loop is one agent's repeated cycle of interpret, act, observe. Orchestration sets the limits and termination conditions around that loop.
- MCP standardizes how an application connects models to tools and data. It carries messages; it does not control execution paths.
- A multi-agent system describes several agents collaborating. It says nothing about who routes work or owns the final result.
This is why ai agent orchestration matters even when a system runs a single agent. Someone still has to enforce retries, permissions, and stopping conditions.
How AI agent orchestration works
Asking how does ai agent orchestration work is really asking how one control loop behaves: plan, route, execute, observe, adapt. An objective enters, gets decomposed into tasks, and each output is checked before the workflow advances. These are the key steps of ai agent orchestration, and each one ends with something a person can inspect.
Plan and route the work
Most objectives cannot be executed in a single agent call. The orchestrator decomposes a goal into discrete tasks, records their dependencies, and schedules what runs sequentially and what can safely run in parallel.
Routing then assigns each task to an agent, model, or tool based on task type, capability, permissions, and current load. A coding task might go to one agent while test generation goes to another, with a reviewer passing last.
Execute with state and checkpoints
State gives a multistep workflow continuity. The orchestration layer tracks the task queue, intermediate outputs, and execution history, rather than trusting a conversation transcript as the source of truth.
Context assembly selects what each model call actually sees: instructions, retrieved data, and only the relevant slice of history. Checkpoints verify progress between stages, so errors surface early instead of compounding downstream.
Observe, adapt, and stop
Every output gets evaluated before the next step begins. On success, state updates and the workflow advances; on failure, the orchestrator retries with new parameters, takes a fallback path, or escalates to a person.
Bounded retries, timeouts, and explicit stop conditions keep an agent from looping forever. Structured logs record what each step did, which is what makes debugging and audit possible later.
Choose from the main orchestration patterns
No pattern is a universal default. The main types of ai agent orchestration differ in where control sits, and each one trades observability against flexibility. Match the pattern to your workflow's complexity and reliability target, not to ambition.
| Pattern | How control works | When it adds too much |
|---|---|---|
| One agent with tools | A single agent keeps responsibility and chooses among bounded tools | When a capability needs separate instructions, context, or permissions |
| Deterministic workflow with agentic steps | Code owns the execution path; models handle interpretive steps | Rarely, because code keeps control of auditable processes |
| Manager with specialists | A primary agent delegates bounded subtasks and synthesizes results | When assignments are vague and coordination costs exceed the work |
| Handoff | Responsibility transfers fully from one agent to another | When transfers are frequent and context gets lost between them |
| Parallel workers | Independent branches run concurrently and results are reconciled | When branches are not truly independent or reconciliation is hard |
| Collaborative review | Several agents contribute to a shared revision with a coordinator | When turns multiply cost and agents reinforce weak assumptions |
Read the table as a complexity ladder. Each row upward adds coordination overhead: another context boundary, another state transition, another place for silent failures to hide.
Two rows deserve emphasis. One agent with tools is sufficient whenever a capability can be expressed as a bounded function with clear inputs and outputs. A deterministic workflow with agentic steps fits processes with known states and high-impact actions, because code keeps control while models supply judgment inside defined boundaries.
The most common mistake is committing to a multi-agent design before a single-agent workflow has proven insufficient. Add agents only when separate instructions, context, permissions, or ownership produce a benefit that one agent cannot deliver as reliably.
Add controls before adding more autonomy
Orchestration earns its keep by making agent work governable. Before scaling autonomy, decide which decisions belong to code, which belong to models, and which belong to people.
- Deterministic boundaries. Keep access checks, schema validation, rate limits, retry counters, and approval gates in code. A model may propose an action; deterministic logic verifies that the action is valid and authorized.
- Clear ownership. Every stage needs one owner who may declare it complete. Unclear ownership produces duplicated work, conflicting answers, and workflows that nobody can sign off.
- Deliberate context design. Store task state in explicit structures, such as retrieved records, tool results, approvals, and pending actions. Assemble context selectively for each call instead of broadcasting full transcripts to every participant.
- Permission gates and human approval. Scope each agent's tools to its role, and pause high-impact actions for human sign-off. A routing decision should never substitute for authorization.
- Logging, evaluation, and recovery. Trace every agent call, and evaluate the execution path as well as the final answer. Use checkpoints and idempotent tools so a failed run resumes safely instead of restarting from zero.
How Atoms helps coordinate a reviewable product-building workflow
The controls above describe an ideal, and applying them to a real build still takes work. Atoms is an AI product-building platform that turns natural-language requirements into editable websites or web applications, and it applies this orchestration discipline to product creation rather than offering a general-purpose agent runtime. Specialized agents coordinate across planning, building, research, and growth, while you preview the result and review each change. Production launches still need human review of content, accessibility, security, integrations, and performance.
- Coordinated multi-agent product builds. Describe the audience, pages, content, and interactions in plain language, and Atoms plans the work and assigns it to specialized agents. Planning, page structure, supporting copy, and media each become a bounded stage with a visible output. You watch the build take shape in a live preview instead of receiving one opaque result at the end. The division of labor mirrors the manager-and-specialists pattern, with the platform holding the routing and shared state.
- Editable, reviewable iteration. Each change request becomes a focused iteration rather than a rebuild from scratch. You can adjust layout, replace media, or refine interactions through conversation, and every revision stays inspectable before you accept it. This keeps the human approval step inside the workflow instead of bolting it on afterward.
- Growth workflows after the build. Dedicated SEO and advertising agents extend the same coordinated workflow past launch. Search strategy, optimization, and campaign planning run from the same platform, so the handoff from building to growth keeps its context instead of starting over.
Women’s And Men’s Suiting Store HARLAN & CO. is a premium suiting ecommerce site presenting refined men's and women's tailoring. It demonstrates Atoms' end-to-end product creation, where specialized agents collaborate across planning, building, and design, the kind of coordinated workflow this guide describes.
Men’s Multi-Category Clothing GRAYSTATE is a minimalist menswear ecommerce site organized around a streamlined wardrobe across multiple categories. It shows how Atoms' coordinated agent workflow delivers a coherent structure and visual experience rather than a set of disconnected pages.
Luxury Evening Wear NOCTURNE is an evening wear ecommerce experience built around elegant formal attire. It illustrates how Atoms keeps a coordinated build editable and reviewable, so the result can be checked before publishing, the human-approval step this guide recommends.
Conclusion
Agent orchestration pays for itself only when it makes agent work easier to control, not when it makes a system look sophisticated. Start with the smallest architecture you can observe, put deterministic boundaries around the decisions that matter, and add agents only when separation earns its overhead. If you want that discipline applied to a real product build, start your next project in Atoms and keep every stage reviewable before you publish.
A little more clarity
Frequently asked questions
01Q1: What is AI agent orchestration?
It is the control layer that decides how agent work is planned, routed, executed, checked, and stopped. It governs the workflow around models and tools rather than generating output itself.
02Q2: Does orchestration require multiple agents?
No. A single agent with tools still needs routing, state management, retry limits, and stop conditions. Multiple agents add coordination requirements, but the need for execution control exists either way.
03Q3: How does agent orchestration work?
An objective is decomposed into dependent tasks, routed to agents or tools, executed with tracked state, and evaluated after each step. Failures trigger bounded retries, fallbacks, or escalation to a person.
04Q4: Which orchestration pattern should a team start with?
Start with one agent and well-scoped tools, or a deterministic workflow with agentic steps for auditable processes. Move to manager, handoff, or parallel patterns only when a single agent proves insufficient.
Share this article
 Posts
